本サイトは、快適にご利用いただくためにクッキー(Cookie)を使用しております。
Cookieの使用に同意いただける場合は「同意する」ボタンを押してください。
なお本サイトのCookie使用については、「個人情報保護方針」をご覧ください。
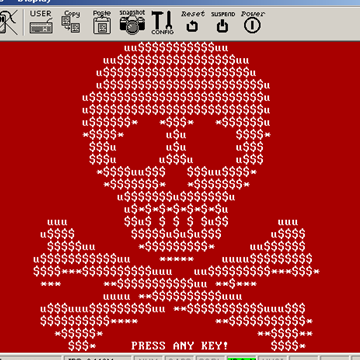
IDA Pro has a feature of cooperating with Bochs virtual machine that enables users to analyze code executed before an operating system is booted up. Recently I had an opportunity to test this feature in practice. This post shows how to use this feature in a real-life scenario.
A few months ago, my co-worker gave me a copy of Petya ransomware that gained attention for its low level feature of encrypting MBRs. Even though I'm not a malware analyst, as a reverse engineering enthusiast, I thought I would try analyzing some of the code with IDA.
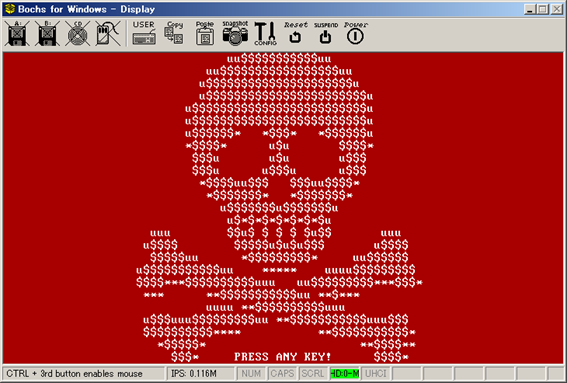
First off, I uploaded the binary to VirusTotal to make sure it's a true copy of Petya. Then I ran it on my victim machine running Windows 7. The machine rebooted immediately after installation and after a fake chkdisk, an ASCII art of a skull appeared on a red screen.
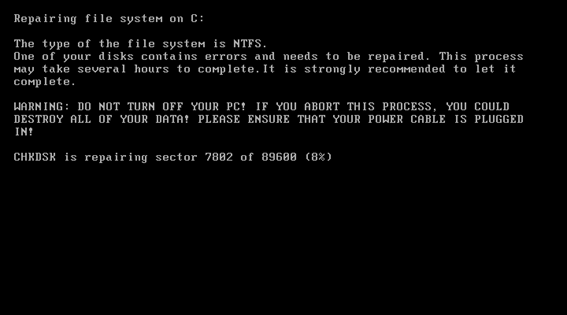
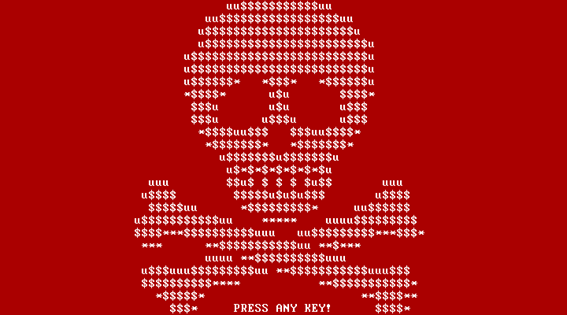
Cool. That's what's expected of Petya. Then I specified the copy of the flat hard disk image as a boot disk image of the Bochs emulator. Again, the skull showed up. That meant the infected MBR was running properly on Bochs.
Next, I loaded the bochsrc configuration file into IDA. It automatically selected IDA loader appropriately and showed the disassembled code in MBR. I could start debugging the code under the Bochs debugger and see how it worked.
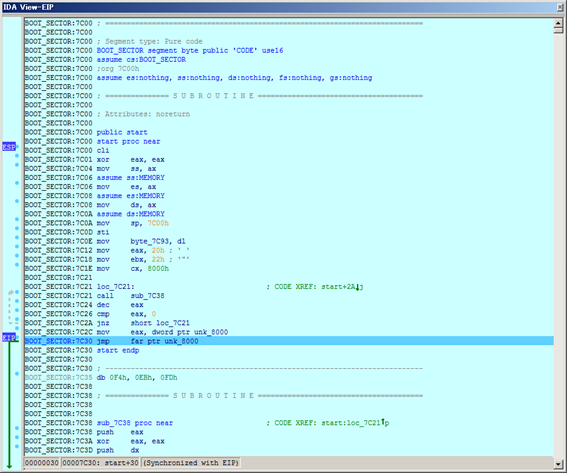
Bochs plugin for IDA is a neat way of analyzing low level code such as MBR and bootloader using IDA. It should be useful not only for reverse engineers but OS developers.
Happy reversing!
おすすめ記事
キーワードで探す
テーマで探す
筆者で探す
- #MBSD
- #MBSD-SOC
- #吉川孝志
- #寺田健
- #高江洲 勲
- #プロフェッショナルサービス事業部
- #小河哲之
- #福田美香
- #R&D部
- #山本健太
- #Alice
- #洲崎俊
- #岩崎 利己
- #浦田秀弥
- #桝屋雅文
- #諌山貴由
- #米山俊嗣
- #白倉 大河
- #廣田 一貴
- #小山凌弥
- #安田祐一
- #金子俊介
- #藤縄 直弘
- #国分裕
- #先端技術セキュリティセンター
- #井餘田 笙悟
- #糟谷 正樹
- #サイバーインテリジェンスグループ
- #坂島悠太
- #服部 慎二
- #一ノ瀬太樹
- #藤田 将弘
- #荒牧 努
- #MI2
- #戸田廉
- #露木 拓巳
- #吉田裕也
- #加藤 創


